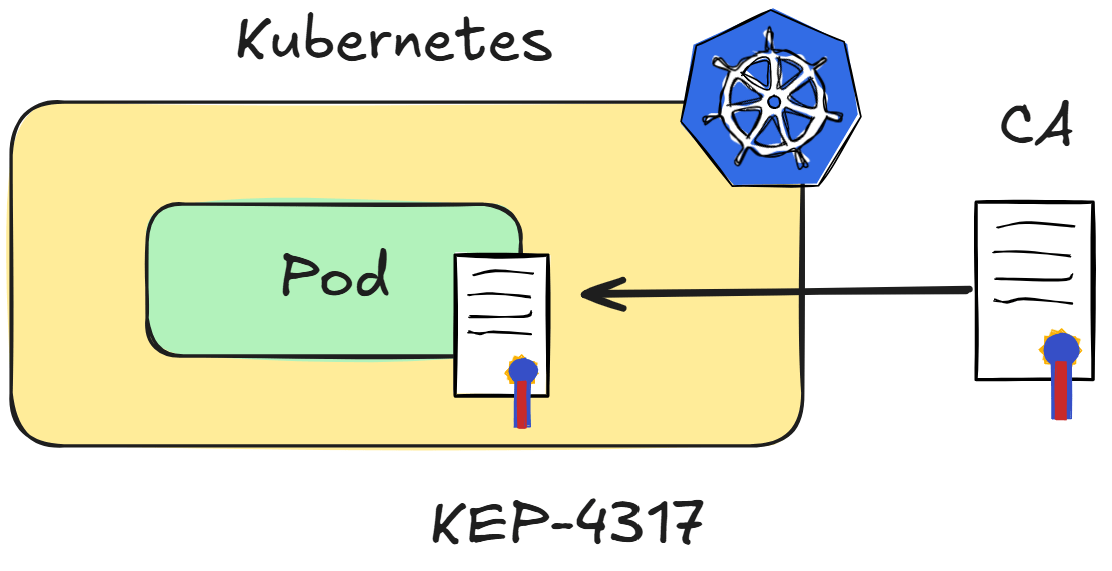
Kubernetes Enhancement Proposals (KEPs) are the process through which new features are added to Kubernetes. These KEPs are divided into three stages: Alpha, Beta, and Stable. In this article, we take a look at KEP-4317, which introduced Pod Certificates.
Kubernetes Pod Certificates | KEP-4317
Pod Certificates became stable with version v1.37 and introduced a new API object called PodCertificateRequest, which you can use to request the signing of a certificate by an external CA. This process should be automated by a controller, but currently there is no official project that implements such a controller. So you are performing the process that the controller would do by hand.
Creating a Certificate Authority
In the first step, you create a Certificate Authority (CA) that will sign the Certificate Signing Requests (CSR) from the Pods. For this, you use the openssl command.
Important: You set the subject to Dominik Custom CA. This is visible later in the signed certificates under Issuer!